A data leak happens when sensitive information becomes accessible to people outside an organization without anyone breaking in. A misdirected email, a storage folder left open to the internet, or an employee with more access than their role requires is enough to cause one.
Defenses built to keep attackers out do not stop exposure that starts inside the organization. Preventing leaks requires cybersecurity controls that focus on the data itself, including where sensitive information is stored, who can reach it, and how it is shared.
This article explains what a data leak is and what causes it. It also gives guidance on how to prevent leaks and respond when one occurs.
What Is a Data Leak?
A data leak (or data leakage) is the exposure of sensitive or confidential data to an unauthorized party, caused by a weakness inside the organization instead of an outside attack. The cause can be human error, a misconfigured system, or misuse of legitimate access. For example, a file shared through a public link exposes its contents to anyone who has the link, without any system being compromised.
Leaks affect data in every state it passes through, from storage to active use. Each state has its weak points, so protection must cover all three.
The three data states and their typical leak points are:
- Data at rest is data stored in databases, cloud storage, backups, and devices. A leak happens when a database or a storage bucket (a container for files in cloud storage) is open to the internet, or when a device with stored files goes missing.
- Data in transit is data moving between systems, users, and services. A leak happens when an email reaches the wrong recipient, a transfer runs unencrypted, or an API returns more data than intended.
- Data in use is data that is open in an application or on a screen. A leak happens through screenshots, copying into unapproved apps, or when printed documents left unattended.
Even if no one opens the data, the exposure itself is the incident, because the business loses control over who can access the information.
Data Leak vs. Data Breach
Both incidents expose sensitive data to unauthorized parties, but they start from opposite directions. A data leak starts inside the organization through an error or misuse of access. A data breach starts outside, when an attacker deliberately gets past security controls through a cyber attack such as phishing, malware, or credential theft.
The following table compares data leaks and data breaches:
| Aspect | Data Leak | Data Breach |
| Origin | Inside the organization. | Outside the organization. |
| Cause | Human error, misconfiguration, or misuse of access. | A deliberate attack on systems or people. |
| Attacker Involvement | Not required for the exposure. | Required. |
| Typical Example | A cloud storage bucket left open to the public. | Ransomware that steals and encrypts company files. |
The two incidents are often linked. Exposed data that attackers find and collect becomes the starting point for a breach (e.g., leaked credentials let an intruder log in to company systems). Preventing leaks also removes one of the easiest paths to a breach.
Causes of Data Leaks
Most data leaks trace back to everyday decisions and settings instead of sophisticated attacks. Several causes often combine in a single incident, such as a vendor copying data into a storage bucket with weak access settings.
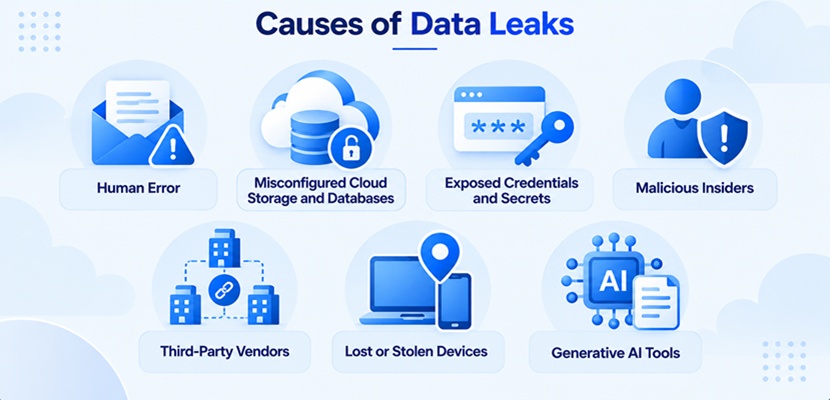
Human Error
Human error causes a large share of data leaks. The mistakes behind these leaks are not malicious, but each one moves data outside the organization's control.
Common examples include:
- Misdirected messages. Emails and attachments sent to the wrong recipient, often through address autocomplete.
- Public sharing links. Documents shared with anyone who has the link instead of with named users.
- Personal cloud accounts. Work files uploaded to personal cloud storage for convenience or remote work.
- Unsecured passwords. Passwords kept in notes, spreadsheets, or browsers instead of a password vault.
- Unlocked devices. Laptops and phones left unlocked and unattended in offices or public places.
- Public Wi-Fi. Work accounts accessed over open Wi-Fi networks that others can monitor.
Social engineering exploits the same mistakes on purpose. An attacker who poses as a colleague or vendor persuades an employee to send sensitive files, and the employee does so believing the request is legitimate.
Misconfigured Cloud Storage and Databases
Cloud storage services and databases rely on access settings that the customer controls. A single permissive setting, such as a storage bucket anyone can read or a database with no password, exposes everything inside it to the internet. Automated scanners, some running on botnets, constantly search for such resources, so outsiders often find an open database before the company does.
Misconfigurations also appear during migrations and testing. A copy of production data in a test environment or a legacy storage system left behind after a migration often has weaker settings than the main environment.
Exposed Credentials and Secrets
Passwords, API keys, and access tokens give direct entry to systems and data. Anyone who finds one of these credentials gains the same access as its legitimate owner.
Secrets most often leak through:
- Source code. Keys hardcoded into applications during development and never removed.
- Configuration files. Credentials stored in plain text alongside application settings.
- Public code repositories. Secrets committed to a public Git repository, where they remain in the history even after deletion from the current version.
- Mobile app builds. Keys embedded in apps that anyone can download and decompile.
Automated tools continuously scan public repositories, so attackers can find an exposed secret within minutes of publication.
Malicious Insiders
Malicious insiders are the deliberate form of insider threats. An employee or contractor with legitimate access copies customer lists, financial records, or other knowledge assets to sell or to use at a competitor. Because the person uses valid credentials, the activity looks like regular work to most security tools.
Third-Party Vendors
Organizations share data with vendors for payroll, marketing, customer support, and software development. Once data sits in a vendor's systems, its protection depends on that vendor's settings and practices. A misconfiguration on the vendor side exposes the company's customers even when its own systems remain secure.
The same risk applies to third-party software connected to internal systems, such as analytics tools and plugins that receive a copy of company data.
Lost or Stolen Devices
Laptops, phones, and USB drives carry copies of emails, documents, and active login sessions. A lost or stolen device exposes everything it stores when the drive is unencrypted and the screen is unlocked. Personal devices used under a bring your own device (BYOD) policy add risk, because the employer has less control over their security settings.
Generative AI Tools
Employees paste code, contracts, and customer details into generative artificial intelligence (AI) assistants to summarize, translate, or debug them. Without a company policy for AI in business, the data leaves company control and may be stored or processed under the tool provider's terms.
Unapproved AI tools used this way are known as shadow AI, and the leaks they create rarely trigger standard monitoring.
Types of Data Commonly Exposed in Leaks
Some categories of data appear in leaks far more often than others. These categories exist in large volumes across many systems, from customer databases to big data servers, multiplying the points where a leak can occur.
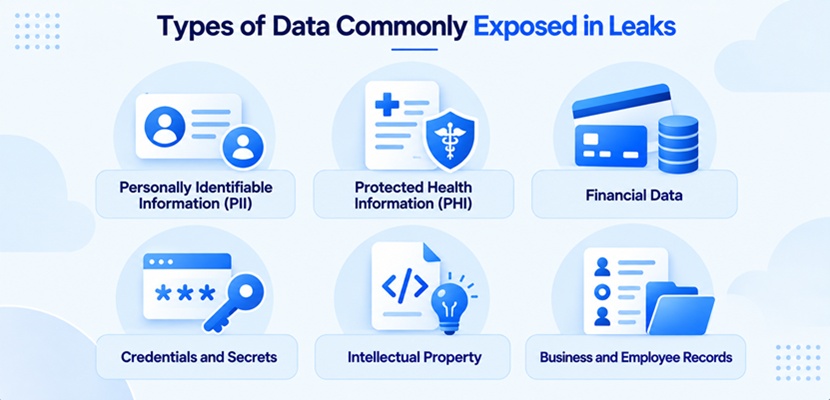
The data types most often exposed in leaks include:
- Personally identifiable information (PII). Names, home addresses, phone numbers, dates of birth, and government ID numbers.
- Protected health information (PHI). Medical records, diagnoses, test results, and health insurance details.
- Financial data. Payment card numbers, bank account details, tax records, and income information.
- Credentials and secrets. Usernames, passwords, API keys, and access tokens.
- Intellectual property. Source code, product designs, research data, and trade secrets.
- Business and employee records. Contracts, internal communications, customer lists, and HR files.
A single leaked file often combines several of these categories. A customer support export, for example, holds PII alongside payment details and account notes, widening the exposure beyond what the file name suggests.
How Data Leaks Are Discovered
A leak doesn’t produce a ransom demand or system outage, so data exposure stays unnoticed until someone notices it. Discovery depends on monitoring coverage and on outside parties that search for exposed data.
Leaks come to light through several channels:
- Internal monitoring. Security information and event management (SIEM) systems and data loss prevention (DLP) tools flag unusual access or large outbound transfers.
- Security audits. Configuration reviews and vulnerability assessments uncover open storage, excessive permissions, and exposed secrets.
- Independent security researchers. Researchers who scan the internet for open databases report their findings to the owner, often before going public.
- Customers and partners. Affected users report their data appearing in unexpected places or scam messages that reference private details.
- Dark web forums and marketplaces. Leaked datasets appear for sale or free download, where threat intelligence services pick them up.
- Law enforcement and regulators. Authorities that encounter leaked data during investigations notify the organization it came from.
The discovery channel shapes the response. A leak found through internal monitoring leaves time to close the exposure before outsiders find it, while one found on a dark web forum means the data has already spread. Without monitoring, an exposure can stay open for months or even years.
Consequences of a Data Leak
The cost of a data leak extends well beyond fixing the setting or process that caused it. Legal, financial, and reputational effects often continue for years after the exposure ends.
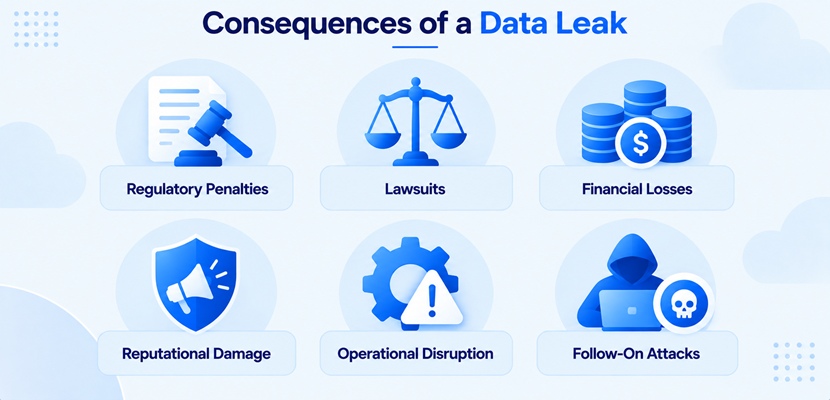
The main consequences include:
- Regulatory penalties. Data protection laws such as GDPR and CCPA allow regulators to fine organizations that fail to protect personal data.
- Lawsuits. Affected customers and employees file individual claims or class actions over the exposure of their data.
- Financial losses. Investigation, notification, and legal costs accumulate alongside revenue lost from departing customers.
- Reputational damage. Customers and partners lose trust in the organization, and some move to competitors.
- Operational disruption. Incident response pulls security and IT staff away from planned work while they review and fix affected systems.
- Follow-on attacks. Cybercriminals use leaked data for phishing campaigns, account takeover, and identity theft against the organization and the affected individuals.
The severity depends on the type of data exposed and the length of the exposure. A short exposure of business contact details causes limited harm, while government IDs or health records exposed for months create risks that affected people carry for years.
How to Prevent Data Leaks
Effective leak prevention works in layers that protect the data itself, control who can reach it, and track where it travels. People form the fourth layer, since training and clear policies address the mistakes that technical controls miss. No single control covers every layer, so companies combine several controls as part of broader business data security.
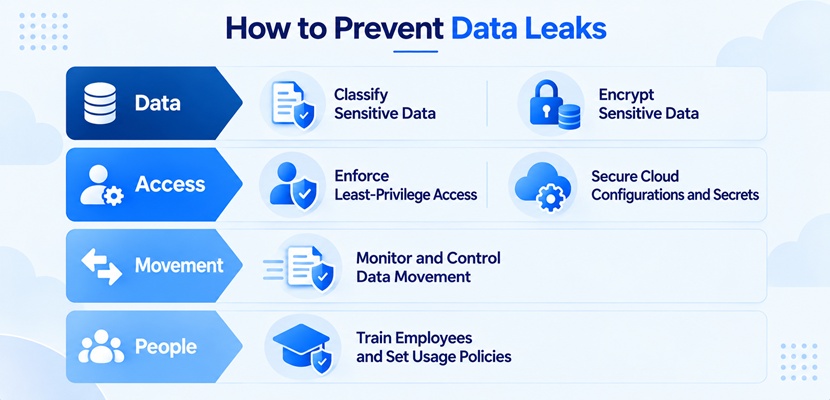
Classify Sensitive Data
Every other control depends on an inventory of what data exists and where it is stored. Data classification labels information by sensitivity so other controls apply the right protection to each category.
Many organizations use a four-level scheme:
| Level | Examples | Required Protection |
| Public | Marketing materials and published reports. | No restrictions. |
| Internal | Internal policies and organizational charts. | Employee-only access. |
| Confidential | Customer records, contracts, and financial reports. | Role-based access control (RBAC) and encryption. |
| Restricted | Health records, payment data, and credentials. | Strict access, encryption, and monitoring. |
Classification also reveals data the business no longer needs. Deleting old records and unused copies reduces the amount of data any future leak could expose.
Encrypt Sensitive Data
Encryption makes data unreadable to anyone without the decryption key. Encrypting data at rest protects files on lost devices and exposed storage, while encryption in transit protects data moving across networks.
Encryption protects data only while the keys remain secure. Good key management practices involve storing keys separately from the data, rotating them on a schedule, and restricting who can use them.
Enforce Least-Privilege Access
Every account with access to sensitive data is a potential leak point. Limiting that access reduces how much data a single mistake or misused account can expose.
The core access controls include:
- Principle of least privilege. Each user, application, and vendor receives only the access its role requires.
- Identity and access management (IAM). Central systems enforce permissions and remove them when someone changes roles or leaves the company.
- Zero trust. Every access request goes through verification instead of automatic trust for users inside the network.
- Multi-factor authentication (MFA). A second verification step prevents a leaked password from opening an account.
Regular access reviews keep these permissions accurate as roles, projects, and vendor contracts change.
Secure Cloud Configurations and Secrets
Cloud resources must start with private settings, and any public access must be a deliberate, reviewed exception. Configuration management is a core part of cloud security. Automated configuration scanning compares settings against security policies and flags storage buckets, databases, or sharing links that have become publicly accessible.
Secrets belong in a dedicated secrets manager instead of in code or configuration files. Secret scanning, a form of automated security testing, checks code repositories for exposed credentials before they can be committed or reach production.
Note: phoenixNAP's Bare Metal Cloud provides a dedicated server with the flexibility of the cloud. Workloads run on single-tenant hardware, giving the organization direct control over access and storage settings. API-driven provisioning keeps server configurations consistent and reviewable, reducing the manual changes that lead to misconfiguration.
Monitor and Control Data Movement
Data loss prevention tools inspect data as it leaves company systems through email, web uploads, and removable media. Based on classification labels, they block, encrypt, or flag transfers that break policy, such as a spreadsheet of customer records sent to a personal address.
Monitoring adds visibility into who accesses sensitive data and when. Alerts on unusual behavior, such as a bulk download at night or access from a new location, help catch leaks in progress. Mobile device management (MDM) extends these controls to laptops and phones, with enforced encryption and remote wipe for lost devices.
Train Employees and Set Usage Policies
Most accidental leaks stem from routine habits, so security awareness training focuses on the situations employees face daily. Practical topics include checking recipients before sending, using approved sharing tools, and recognizing requests for data that bypass normal channels.
Clear policies support the training. An acceptable use policy names approved AI tools and defines which data never goes into a prompt, while a device policy sets the requirements for personal phones and laptops used for work.
What Should Businesses Do in Case of a Data Leakage?
A confirmed data leak requires a fast, structured response. The goal is to stop the exposure, understand its scope, and meet legal obligations without destroying the evidence needed for the investigation. An incident response plan prepared in advance defines roles and decisions, so the response follows an agreed process instead of improvised choices.
1. Contain the Exposure
Close the source of the leak first. Depending on the cause, that means making the storage private, revoking shared links, or disabling the account involved. Immediately rotate any exposed credentials. Until the old credentials stop working, anyone who copied them can still pass authentication. During containment, capture logs and a copy of the affected configuration, since investigators need them to reconstruct what happened.
2. Assess What Was Exposed
Determine the full scope of the leak before deciding on notifications. The findings define who must be notified and which controls need fixing.
The assessment covers:
- Data types. The categories of data involved, such as PII, credentials, or health records.
- Affected people. The customers, employees, and partners whose data leaked.
- Exposure window. The date the exposure began and how long the data stayed reachable.
- Access evidence. Any views or downloads by unknown parties recorded in the access logs.
When logs do not exist or do not go back far enough, treat the data as compromised.
3. Notify Affected Parties
Data protection laws in many jurisdictions require organizations to report leaks of personal data to regulators and affected individuals within set deadlines.
The rules depend on the jurisdiction, the industry, and the type of data involved, so legal counsel must guide the timing and content of every notice. Notices to individuals explain what happened, which data was involved, and what steps people should take to protect themselves.
4. Fix the Root Cause
Closing one exposure does not prevent the next. Identify why the exposure happened, whether through a missing review step, an unclear policy, or an unmonitored system.
Correct the underlying process instead of the single affected resource. Check whether the same weakness exists elsewhere, since a configuration mistake made once is often repeated across similar resources.
5. Review and Update Controls
Once the incident closes, review which controls failed and which ones worked. Update classification, access rules, and monitoring based on the findings. Add the scenario to future training and response drills.
What Should Individuals Do if Their Data Gets Leaked?
Users affected by a leak cannot fix the exposure themselves, but they can reduce the chance of the leaked data being misused. The right steps depend on what was exposed. The company's notification will list the affected data and any support it offers, such as free credit monitoring.
After learning about a leak, take the following steps:
- Change exposed passwords. Replace the leaked password on every account that uses it. Use a strong, unique password for each account, and keep passwords in a password manager.
- Enable multi-factor authentication. Turn on multi-factor authentication for email, banking, and other important accounts, so a password alone cannot open them.
- Freeze your credit. If government ID numbers or financial details were leaked, ask the credit bureaus to freeze your credit. A freeze makes it much harder for someone to open new credit accounts in your name.
- Watch for phishing. Treat unexpected emails, texts, and calls that mention personal details with caution. Scammers use leaked data to make their messages convincing and to lure people to malicious websites.
- Monitor financial accounts. Check bank and card statements for unfamiliar transactions. Immediately report any suspicious charge to the merchant.
- Report identity theft. If someone uses the leaked data to open accounts or make purchases, report it to the police or the national identity theft authority.
Leaked data does not expire, so periodic account and credit checks remain useful long after the initial notice.
Notable Data Leaks
Recent leaks show how ordinary settings and oversights expose data at scale. The following three incidents each stem from a different cause, and each organization responded differently.
Volkswagen Cariad
In December 2024, reports revealed that Cariad, the software subsidiary of Volkswagen Group, had exposed data from about 800,000 electric vehicles for months. The vehicles belonged to Volkswagen, Audi, Seat, and Škoda owners, most of them in Europe. A misconfigured Cariad system revealed the access credentials for the cloud storage environment that held several terabytes of vehicle data.
An anonymous whistleblower alerted the Chaos Computer Club (CCC), a European hacker association, which investigated the exposure with the German magazine Der Spiegel. The data linked vehicles to owners' names, email addresses, phone numbers, and home addresses. For about 460,000 vehicles, it also included precise location histories that showed where drivers lived, worked, and parked.
The CCC notified Volkswagen on November 26, 2024, and Cariad fixed the issue within hours. The company stated it found no indication that third parties had misused the data and that accessing it required considerable expertise. The quick fix and coordinated disclosure limited the damage, but the incident drew criticism from the CCC over how much movement data the carmaker collected and stored.
Illinois Department of Human Services
In January 2026, the Illinois Department of Human Services (IDHS) disclosed that an internal mapping website had exposed personal data on more than 700,000 residents. Staff had built maps on a public mapping platform to plan where to place offices and resources and incorrect privacy settings made those maps publicly viewable.
The exposure began as early as April 2021 and lasted until IDHS discovered it on September 22, 2025. It affected 672,616 Medicaid and Medicare Savings Program recipients, whose addresses, case numbers, and demographic data were visible without names. For another 32,401 people served by the Division of Rehabilitation Services, the maps also showed names, addresses, and case statuses.
The mapping platform kept no record of who viewed the maps, so IDHS could not determine whether anyone accessed the data during that period. The agency reviewed every exposed map, blocked uploads of identifiable customer information to public mapping platforms, and adopted a Secure Map Policy. For affected residents, the long exposure window means the data could have been copied at any point.
Tea App
In July 2025, Tea, a dating safety app for women that had just reached the top of the U.S. App Store, left user verification images in an unsecured cloud storage bucket. Users of the 4chan forum found the bucket on July 25 and shared its contents publicly. The bucket belonged to a legacy storage system that the company had not migrated to its newer infrastructure.
The exposure included about 72,000 images, among them roughly 13,000 selfies and photos of government-issued IDs that users had submitted for account verification. Some images still contained GPS metadata, which people online used to map users' locations. Days later, a second exposed system revealed about 1.1 million private messages between users.
Tea confirmed the incident the same day, brought in external cybersecurity experts, and stated that only users who signed up before February 2024 were affected. The leak did not include email addresses or phone numbers. Several class action lawsuits followed, alleging that the app kept verification selfies it had promised to delete.
Data Leak FAQ
Organizations and the people whose data is exposed tend to ask the same practical questions. The most common ones concern how leaks differ from breaches, what the law requires, and how to check whether personal data was exposed.
What Is the Difference Between a Data Leak and a Data Breach?
A data leak exposes data through an internal mistake or misuse of access, with no attacker needed. A data breach happens when an attacker deliberately gets past security controls to steal or access data.
How Do I Know if My Data Was Part of a Leak?
In most jurisdictions, companies that confirm a leak of personal data notify affected people by email or letter. Lookup services such as Have I Been Pwned check whether an email address appears in known leaked datasets. Unexpected password reset emails, login alerts, or scams that mention personal details are also signs of a leak.
Are Businesses Legally Required to Disclose Data Leaks?
Yes, in most cases. The EU’s General Data Protection Regulation (GDPR) requires organizations to report a personal data breach to the supervisory authority within 72 hours of becoming aware of it, and to inform affected people when the risk to them is high. Its definition covers accidental disclosure, so a leak counts even without an attacker.
All 50 U.S. states have their own notification laws, and sector rules such as HIPAA add separate requirements for health data.
What Is the Biggest Data Leak of All Time?
The most extensive data leak, also known as the Mother of All Breaches (MOAB), was discovered in January 2024. The exposed database held about 26 billion records compiled from thousands of earlier breaches and leaks, and its owner attributed the exposure to a firewall misconfiguration. Yahoo's 2013 breach, which affected three billion accounts, remains the largest incident at a single company.
Stopping Data Leaks Before They Start
Data leaks rarely need an attacker, making them one of the most preventable security incidents an organization faces. Most trace back to a misconfigured setting, an excessive access right, or an unsafe habit. Start by identifying where your most sensitive data lives and who can reach it, and close the gaps that expose it to people who should not see it.